
Future-Proof Machines Start with Cyber-Secure Components
Understand what the CRA means for component selection, lifecycle management, and long-term system security.
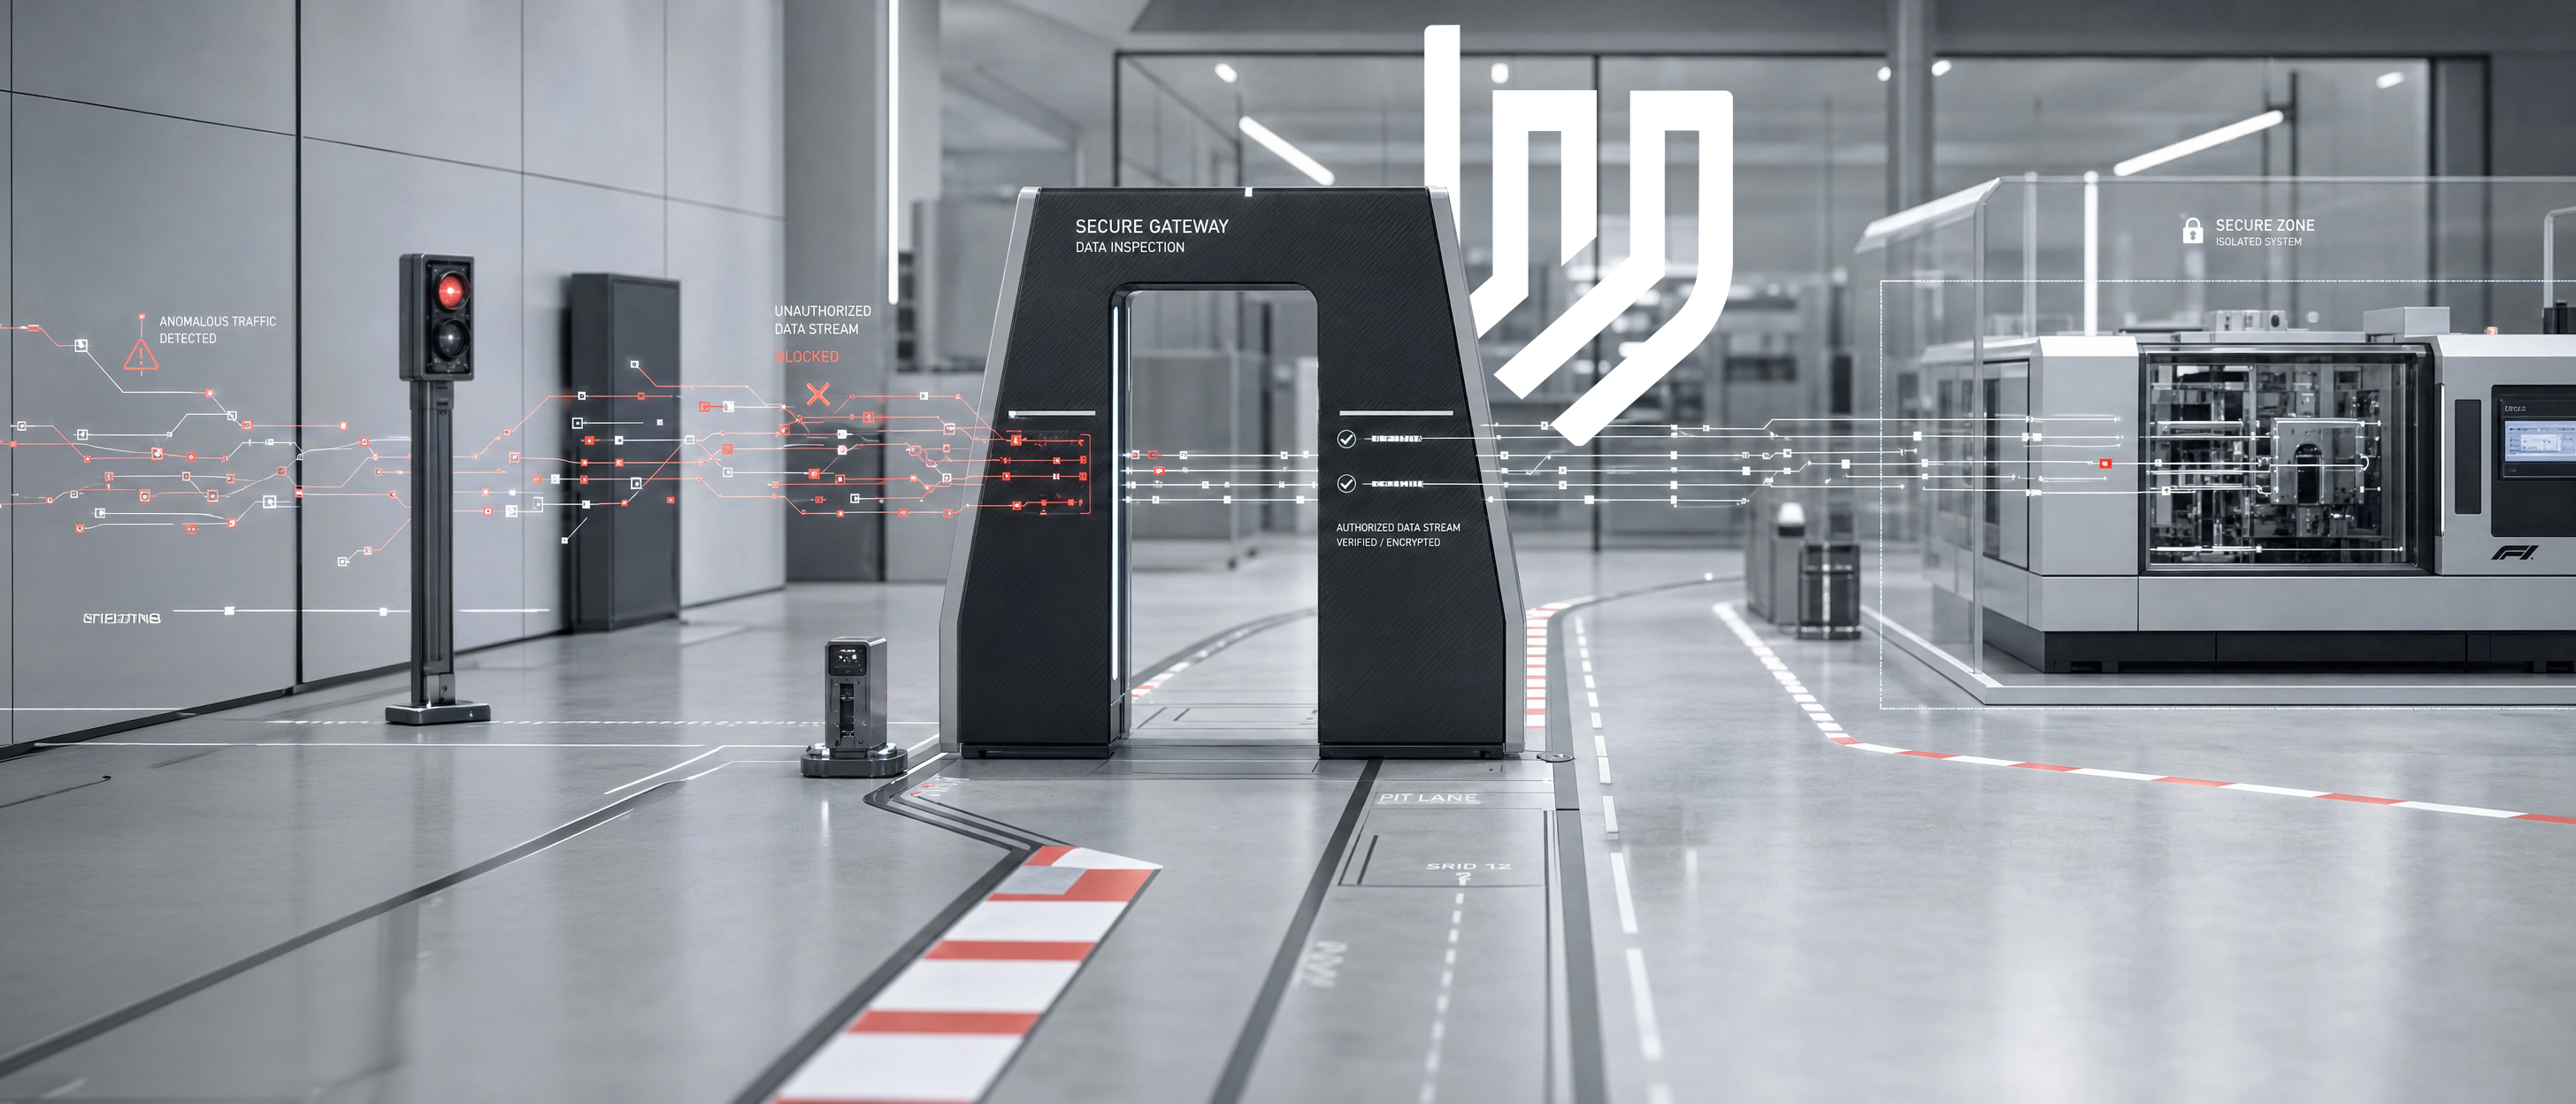
The machines of tomorrow must do more than perform reliably. We expect them to remain secure, maintainable, and adaptable throughout their entire lifecycle. As connectivity continues to expand across automation systems, cybersecurity becomes an engineering discipline that influences component selection, system architecture, update strategies, and long-term operational resilience.
What is the Cyber Resilience Act?
Cybersecurity is a fundamental requirement for reliable and sustainable machine operation. As industrial systems become increasingly connected, protecting data, ensuring system integrity, and enabling controlled interaction between components are essential for stable and long-term operation.
Industry regulations such as the European Cyber Resilience Act (CRA) establish cybersecurity requirements for products with digital elements placed on the European market.
Future-proof machines are designed with these principles in mind. They support secure firmware updates, ensure predictable communication between components, and maintain system integrity throughout their entire lifecycle. This requires a shift from isolated product checks toward a consistent, system-level approach.

Future-proof machine design means
Secure firmware update mechanisms, controlled and predictable communication behavior, and end-to-end system integrity help ensure the protection and stability of your industrial systems.

Why Cybersecurity matters for machines
Designed for connected industrial environments: As systems become interconnected across production, IT, and cloud layers, reliable and predictable communication is essential. At the same time, machines must remain secure and maintain their integrity throughout long operational lifecycles.

Secure architecture for stable and long-term system performance
Security throughout the lifecycle: Integrated security, continuous protection, and controlled update strategies ensure long-term system resilience.
Our Products
19 versions
|
Order code
|
Price | Order Code | Housing material | Actions |
|---|---|---|---|---|
|
330 EUR
Please login for individual prices.
|
BNI00L1 | Plastic | ||
|
490 EUR
Please login for individual prices.
|
BNI00KH | Plastic | ||
|
530 EUR
Please login for individual prices.
|
BNI00K6 | Metal | ||
|
130 EUR
Please login for individual prices.
|
BGL007Y | Metal | ||
|
140 EUR
Please login for individual prices.
|
BGL007Z | Metal | ||
|
150 EUR
Please login for individual prices.
|
BGL0080 | Metal | ||
|
160 EUR
Please login for individual prices.
|
BGL0081 | Metal | ||
|
400 EUR
Please login for individual prices.
|
BNI00L7 | Plastic | ||
|
455 EUR
Please login for individual prices.
|
BNI00L8 | Metal | ||
|
530 EUR
Please login for individual prices.
|
BNI00L9 | Plastic |



Edit columns
Please select which columns should be displayed.
How Balluff supports CRA implementation
 Lifecycle Capability built into the product
Balluff products are designed for long-term secure operations.
Easily accessible updates from the Balluff Update Platform
Reduced service effort: System-level update management
Architectural stability defined behavior already in design phase
 Coordinated Vulnerability Handling
Balluff ensures structured and reliable vulnerability handling.
Dedicated PSIRT (Product Security Incident Response Team)
Cooperation with recognized institutions (e.g. CERT@VDE)
Defined escalation and communication processes
 Transparency and practical guidance
We translate regulatory requirements into usable engineering information.
Clear integration context: Defined intended use and system limits
Practical documentation: Regulatory requirements mapped to real applications
 Secure Development you can rely on
Cybersecurity is embedded throughout product development.
Secure Product Development Lifecycle (SPDLC) aligned with IEC 62443-4-1
Information security based on IEC 27001
What makes a product CRA-Ready?
A CRA-ready product is designed to support manufacturers in implementing CRA-relevant cybersecurity requirements through built-in lifecycle capabilities, secure development processes, structured update mechanisms, and transparency regarding intended use and system integration.

Built for Secure Lifecycle Management
Security built into products from the start.

Easy access to security documentation and guidance.

Long-term maintainability with structured security lifecycle management.

Defined firmware update strategies and vulnerability handling processes.

FAQs on the Cyber Resilience Act (CRA EU 2024/2847) for Machine Builders, Plant Manufacturers, and System Integrators
Disclaimer: All answers given within this FAQ serve as a general orientation only and are not a legal or technical counseling. Balluff cannot be held liable for any completeness or correctness of this information provided here or for decisions made upon that information. We reserve the right to update this information as regulatory requirements evolve and our implementation of CRA-compliance measures progresses.
-
CRA and Machinery Manufacturing – What does it mean for you?
The Cyber Resilience Act (CRA EU 2024/2847) introduces mandatory cybersecurity requirements for products with digital elements. Its objective is to ensure that products are securely developed, operated, maintained, and supported throughout their entire lifecycle.
For machine builders, cybersecurity therefore becomes an integral part of product development, risk assessment, and supplier management.
-
Why is the CRA relevant to you?
Most modern machines today contain digital components such as:
Sensors and actuators
IO-Link devices and IO-Link masters
Fieldbus and Ethernet components
Camera systems
Embedded software and firmware
Industrial PCs
As a result, many machines fall within the scope of the CRA. In addition, every machine builder must take the cybersecurity risks of integrated components into account as part of their duty of care.
-
When does a machine or system fall under the CRA?
A machine typically falls under the CRA if, cumulatively:
It contains digital elements.
It is made available on the EU market.
It exchanges data directly or indirectly with other devices or networks.
Even an indirect connection is sufficient, for example, through Ethernet, PROFINET, PROFIBUS, USB, Wi-Fi, Bluetooth, NFC, remote maintenance systems, industrial PCs, or gateways. A direct Internet connection is not required.
If a machine processes, stores or transmits data, the CRA is likely to apply.
-
Do existing machines or systems need to be replaced?
No. At the time this document was last updated, there is generally no requirement to replace machines that are already installed.
The CRA primarily applies to products with digital elements that are newly placed on the market after the introduction of the CRA or that undergo substantial modifications after that date.
-
How do Balluff CRA-Ready products help meet CRA-Requirements?
Since the CRA will only become fully applicable on 11 December 2027, no manufacturer can currently declare formal CRA-conformity for products.
We therefore use the term "CRA-Ready" for products where, for example:
A cybersecurity risk assessment has been conducted
Security requirements aligned with IEC 62443 have been implemented
Security updates are planned and supported
Structured documentation for secure integration is available
Future CRA requirements have already been considered
A Product Security Incident Response Team (PSIRT) is available as a point of contact for vulnerability reporting
The CRA-Ready products we provide already establish the foundation for long-term secure integration. This reduces the effort required for risk assessments, supplier audits, and future compliance documentation.
-
Does a CRA-Ready product replace your responsibility for a CRA-Compliant machine or system?
No, it does not. The machine builder remains the manufacturer of the overall system and is responsible for assessing the cybersecurity risks of the complete machine in its entirety, even when integrating CRA-Ready products. This responsibility also remains when using formally CRA-compliant products.
CRA-Ready products, and later CRA-compliant products, support machine manufacturers because of suppliers such as Balluff:
Implement security requirements for their products
Monitor vulnerabilities
Provide security updates
Document relevant security information
This information can be used as part of the machine's cybersecurity risk assessment and technical documentation.
-
Why do different products have different security measures?
The CRA follows a risk-based approach. Not every product requires the same security features.
The required measures depend on several factors including:
Product functionality
Degree of connectivity
Operating environment
Expected service life
Potential impact of a cyberattack
Therefore, an IO-Link sensor requires different security measures than an IO-Link master, a smart camera, or software.
Security measures are determined based on a cybersecurity risk assessment.
-
How do the CRA (EU 2024/2847) and the Machinery Regulation (EU 2023/1230) work together?
The CRA and the Machinery Regulation (which replaces the Machinery Directive 2006/42/EC on 20 January 2027) pursue different objectives but complement each other.
CRA
Machinery Regulation
Focus on cybersecurity
Focus on safety
Protection against cyberattacks
Protection against hazards to persons
Products with digital elements
Machinery and related products
Many cybersecurity measures also support compliance with Machinery Regulation requirements.
Examples include:
Protection of control systems
Software integrity
Protection against tampering
Secure communications
However, compliance with the CRA does not automatically ensure compliance with the Machinery Regulation.
-
How should you handle vulnerabilities in purchased products, such as Balluff components?
When a vulnerability becomes known, Balluff will communicate available mitigations and updates via CERT@VDE
As a machine builder, plant manufacturer, or system integrator, you must assess whether vulnerability is exploitable within the specific application and determine if additional protective measures are required.
Responsibility for the overall machine remains with the machine manufacturer, at any time.
Balluff supports customers through:
Vulnerability information (Security Advisories in CSAF format via CERT@VDE)
Security updates provided through the Balluff update platform
PSIRT contact options
A coordinated vulnerability disclosure process
All information about the Balluff PSIRT and how to report vulnerabilities can be found here: Secure. Transparent. Reliable: Product Security at Balluff
-
What should you do if you discover a vulnerability in one of our products or software products that affects your machine or system?
If you identify vulnerability in one of our products or software products during testing, a security audit, or by any other means, and that vulnerability affects your machine or system, please report it directly to our Product Security Incident Response Team.
By reporting the vulnerability to our PSIRT, you enable:
A confidential assessment of the issue
Coordination of potential remediation measures
Provision of security information and updates
Responsible and coordinated vulnerability handling
-
What is the difference between the CRA and NIS2 (Network and Information Security Directive)?
Both regulations contribute to strengthening the cybersecurity of products, machinery, and infrastructure. However, they address different areas of cybersecurity.
CRA
NIS2
Applies to manufacturers
Applies to organizations and operators
Defines requirements for products with digital elements
Requires organizational and technical security measures
Focuses on product security
Focuses on organizational and operational security